Exclusive WolfSec0x0 Interview on 2026 MeshAgent Cheating Scandal
GipsyTeam
Today, 15:28
A cybersecurity expert going by WolfSec0x0 talked to us about the investigation of the MeshAgent scandal, shared new details, and offered some tips on how to protect your bankroll.
In late September, user X, nicknamed WolfSec0x0, posted a Twitter thread about hacking high-stakes players using the MeshAgent remote viewing program.
With MeshAgent, the attackers gained access to the victim's computer and were able to see their hole cards during a game. It would be like playing with Mike Postle, if he was looking over your shoulder instead of into his crotch.
After gaining access to players' computers and cards using the Mesh Agent program, Canadian Paul Gregg robbed over several years, perhaps with other robbers. On the WPN network alone, the criminals got almost $900,000.
In an interview with GipsyTeam, the author of the investigation explained that he has been professionally involved in cybersecurity for over 10 years, but he's familiar with poker extends beyond his professional career.
He started playing as a teenager, then moved to live cash games between $2/$5 and $10/$25. WolfSec0x0 now plays NL200–NL1,000, but just as a hobby. His primary role is managing teams responsible for automation and threat detection systems.
Over the years of communicating in poker Discord communities, he's earned the trust of prominent high-stakes players and has already helped some of them recover after hacks.
So, when a group of regulars discovered a suspicious program on their computers, they turned to him for help.
We spoke with WolfSec0x0 about the details of the high-profile case, the possible scale of the issue, and online poker security in general.
How MeshAgent was Found & Where Infected Version Came From
— Can you walk us through how this case started from your perspective?
What did the high-stakes community first bring to you, and what was the first thing you found that made you realize this was more than just a suspicious poker account or an isolated malware infection?
I was contacted a by a small group of HS players that I've worked with in the past on some previous cybersecurity issues, although I believe the first POC was someone that knew that I had worked with them, not that I'd worked with directly.
They had already started investigating for themselves, using AI assistants to makeup for any technical shortcomings. When I arrived, they had done enough already to understand what the MeshAgent RMM tool was and where it was calling out to. Additionally, we had enough players reporting that they too were infected which make it unlikely that this was more of a one-off type infection. From there, I started to hone in on similarities and potential initial access avenues.
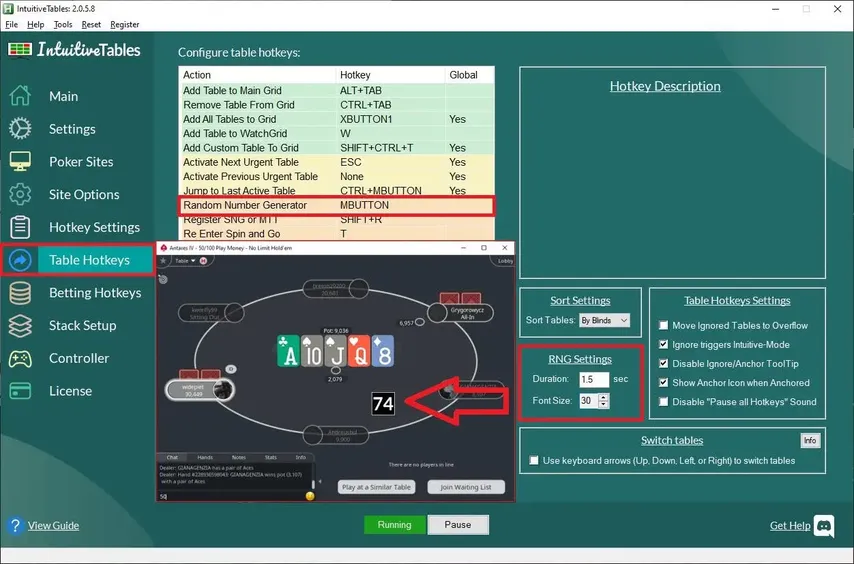
Once I had this information, I was able to create some triage scripts for the players to run to start checking logs on their PC's. This is how we discovered the compromised IntuitiveTables installer (which was downloaded from the legitimate source).
— How did you confirm that the installer downloaded from the legitimate source was compromised? And do you know how it became infected in the first place?
We could see the download source in logs and artifacts on the compromised computers, confirmed it with a number of people.
IntuitiveTables is a program for setting poker tables and automating multi-tabling operations.
The second compromised program with similar functionality was Jurojin.
In early October, Jurojin developers published their own technical report on the hack. According to their findings, from June 2025 to January 2026, the attacker periodically replaced updates for a specific group of users. The company discovered 92 different instances of distribution of modified archives. Sometimes, the replaced file remained accessible for only a few hours, after which it was replaced with a normal version.
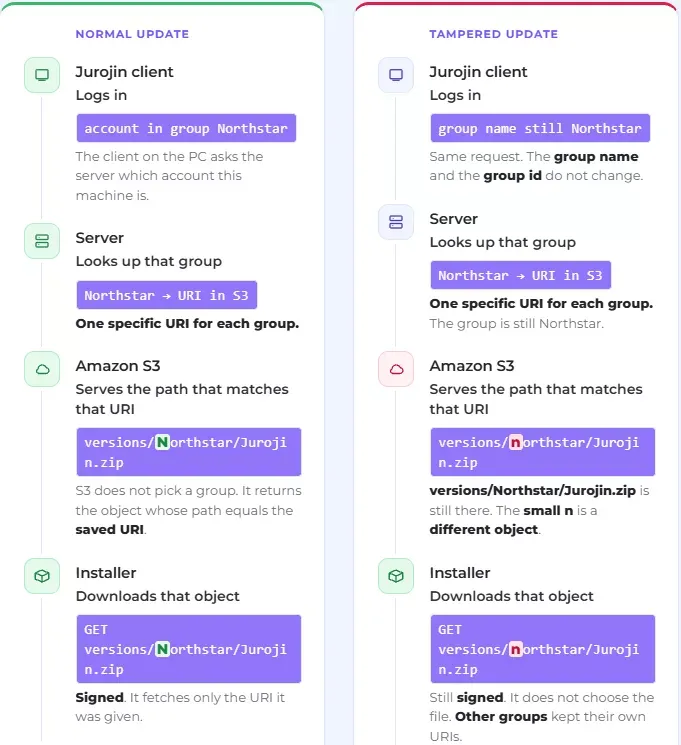
To redirect the download, the attacker changed one letter in the Amazon S3 archive address. As a result, for certain users, the program downloaded the file from a different location while maintaining the normal update mechanism. However, not every modified archive contained the remote access tool.
The normal Jurojin update download path (left) and the one modified by the attacker (right)
— Have you figured out how the IntuitiveTables installer was compromised?
Partly. We know what was done, but not yet how the attacker got in (for intuitivetables – they have not released any information to the public). On 3 March 2026 a backdoored version of IntuitiveTables was built and signed with the company’s own valid code-signing certificate, and at least one victim downloaded it straight from the official website. It was compiled from newer source code than the clean version before it.
So this wasn’t someone repackaging an old installer: the attacker appears to have had access to the source code and the signing process. The hidden code checked the player’s screen name against a target list and only installed the remote-access software on a match. Everyone else using that build would have seen nothing unusual. How the build pipeline was compromised is still an open question for IntuitiveTables and law enforcement.
On the earlier cases: the oldest infection we’ve confirmed from this operator is from November 2022, well before the poker-software route. Those early victims were hit in more traditional ways: a foothold on the PC, a trick to get admin rights, password-stealing tools, and a disguised copy of the remote-access agent. The poker-tool route came later.
Jurojin’s update channel was serving malicious packages from June 2025 into 2026, and the IntuitiveTables build followed in March 2026. I haven’t confirmed any 2022 infections myself, but this operator has clearly been active for years and was spreading malware since at LEAST 2022 that I know of.
100+ Confirmed Cases & Hundreds of MB of Data from Players' Computers
— Your first report mentioned around 30 affected computers. Do you have an updated number?
And do we know how many of those players were actually targeted at the tables?
There’s no final number yet, and there may never be an exact one. More than 100 are now confirmed, up from about 30 in our first report, and I suspect somewhere between 300 and 1,000 in total. Jurojin’s own records show several hundred accounts were pointed at the malicious download at least once, and they describe that as a minimum. Being exposed isn’t the same as being infected, but that’s why I put the range where I do.
On targeting: I still believe every victim was chosen to some degree, based on who they are (high stakes or high profile) and where they play (GGPoker, WPN, CoinPoker and others). The IntuitiveTables backdoor is the clearest example: it only installed the agent if the player’s screen name was on a target list.
We also see remote-desktop sessions on victims’ PCs uploading hundreds of megabytes at a time, which fits someone watching live play. But only the poker rooms can tie those sessions to specific hands, because only they know who was sitting at the table. That’s the most important missing piece.
How do you think poker rooms should have handled those reports?
I can’t speak to that specific report or what GGPoker did with it internally. In general, I think rooms should treat credible integrity reports as possible security incidents, not just player complaints: acknowledge them, preserve the data and follow up with the person who reported it.
This case also shows why the usual checks can miss this kind of cheating. It ran through malware on the victims’ computers, so the account that benefited could be on a perfectly clean machine with normal-looking play. Rooms have to look from the victim’s side as well: which accounts keep sitting with the same players, and who wins improbably well against them specifically.
A number of voices in this community do a great job of raising the alarm when something is off, and I hope they’re given more credit going forward – I saw the WPT team had put out a nice project dedicated to finding super users.
WolfSec0x0 is likely referring to A5 Labs' AceGuardian Research. The company has published open source code for tools for detecting suspicious play based on hand histories. GipsyTeam previously recounted a conversation between A5 Labs' founders and Joe Ingram about combating bots and other forms of cheating.
Guests of Joe Ingram's podcast were the founders of A5 Labs, John Andress and Thanh Tran, who have been involved in online gambling security for many years. They discussed common types of fraud and which types of bots are the most dangerous for players.
— How could rooms and independent researchers work together without putting players' privacy at risk?
Honestly, there’s very little incentive for poker sites to work with third parties, so I think it’s up to each site’s player base to demand accountability and collaboration. But it can be done without putting anyone’s privacy at risk.
A lot of what matters contains no personal data at all: malware file names, domains, server addresses and attack techniques can be shared freely between rooms and researchers, the same way banks share fraud indicators. Where player data is needed, consent works.
In this investigation players shared their own data voluntarily, we referred to them only by handle, and their identities went to a site, vendor or police force only with their permission. Rooms could also make independent research easier without exposing anyone. They could use stable anonymous IDs in hand histories, so patterns can be studied without revealing who’s who, and have a security contact that actually responds.
— WPN recently introduced ScreenShield, a feature designed to stop other software from capturing poker tables. What do you think of it? Would it be enough to prevent attacks like the MeshAgent case?
I haven’t tested it myself, and I’ve heard secondhand that it isn’t very effective. It probably helps with the proverbial lowest-hanging fruit.
— Which three poker rooms do you personally think are the safest for players right now, and why?
Without a deep understanding of the security measures each site uses, it’s tough for me to rank them.
What I can say is that the security teams that reach out to learn more and take a proactive approach are the ones I trust most to find and remove malicious users and cheaters. If I were choosing where to play, I’d look for a site that responds quickly when players or researchers report something, is open about what it finds, and refunds players when cheating is confirmed.
Compensation for Affected Players
Following the publication of the investigation, Jurojin developers acknowledged the security issue with their software and apologized to users.
They also addressed the topic of compensation:
"Compensation and refunds are the rooms' responsibility. They are the ones who can validate fair play and analyse game patterns. We cannot do that analysis, and we should not. The rooms hold the hand histories and the account records that a refund depends on."
— Do you agree? Who do you think should pay for the losses in cases like this?
I’m not a lawyer, so I’ll leave the question of legal responsibility to others.
In practice I see two routes.
In the short term, the poker rooms are best placed to act. Only they can see which accounts sat with victims while their screens were being watched, and they can freeze and confiscate those winnings and pay victims back, as rooms have done in past bot and superuser cases.
Ultimately, though, I believe the best shot at recovering anything beyond that is law enforcement action against the person behind this. I’d encourage every affected player to file a police report with an estimate of their losses (IC3 in the US, Action Fraud in the UK, or their local police) so the cases can be linked.
How Players Can Protect Themselves
— What are the two or three most important things online poker players should do to keep their computers safe?
Be proactive. Learn the basics of PC security: what’s installed, what starts with Windows, and whether there’s any remote-access software on your machine that you didn’t put there. Red flags from this case include a “Mesh Agent” service, remote-access tools you don’t recognise, and Windows Defender exclusions you didn’t add. AI assistants are great for helping you understand what you’re looking at, but never run commands or scripts you don’t understand, even if a website or a “support” person tells you to. That’s one of the most common ways people get infected.
For professional players, use a dedicated, clean machine for poker only. No email, general browsing, downloads, cracked software or crypto on it, and keep your list of poker tools as short as possible. In this case the malware came through popular poker tools. One was signed with the developer’s real certificate and downloaded from the official website, so “signed” and “official” aren’t guarantees. Every tool you add is another way in.
For top-stakes players, treat your computer and accounts the way a business would. Use a password manager. Keep crypto in a hardware wallet. Bring in outside security to audit your setup regularly, and have a plan for when something goes wrong.
Recovery for anyone that was affected: Working from a different, clean device, change your email password first and sign out every session, then do the same for everything else. Then wipe and reinstall the PC.
— Beyond MeshAgent, what worries you most about online poker security today? Are you working on any other poker-related investigations you can talk about?
What worries me most is that this will keep happening, and faster, because AI is making it easier for attackers to build and run campaigns like this.
The other big worry is the supply chain. Serious players run several third-party tools (HUDs, table managers, trackers, solvers), usually with full admin rights and often from very small developers. Compromise one of them and you can reach hundreds of high-stakes players at once, and in this case two different tools were used.
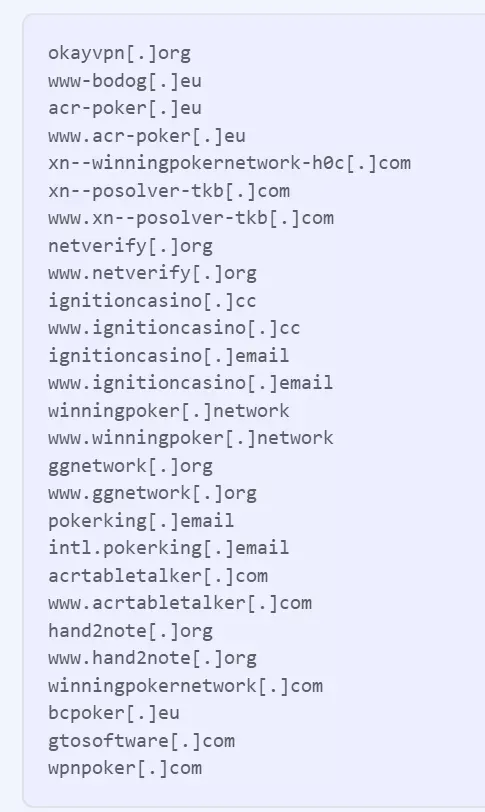
We also found look-alike domains for popular poker tools on the attacker’s network, such as hand2note(.)org (the real site is hand2note.com) and a PioSolver look-alike spelled with a dotless “ı”.
Fake domains from the list published by Jurojin
Always check the address before you download anything.
How to Check Your Computer Right Now
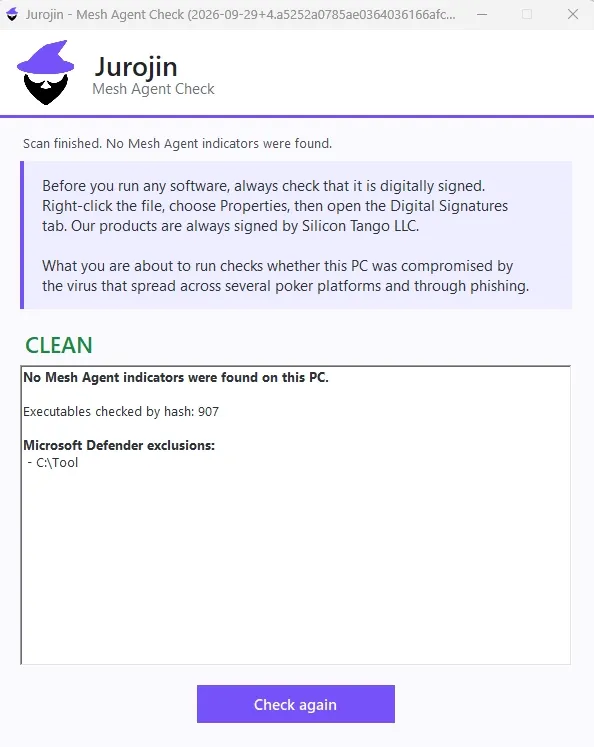
You can check your computer for the Mesh Agent using Jurojin Mesh Check (clicking on the link will immediately start the download from the official Jurojin website).
The absence of traces of intrusion does not guarantee that the computer has not been infected.
If there is serious reason to suspect a hack, Jurojin developers recommend a complete reinstallation of Windows.
You will be able to leave comments, rate posts, participate in discussions and increase your poker level.
If you prefer a four-colour deck or want to turn off avatar animation, change your profile settings.
You will have an access to bookmarks, staking and other useful poker tools.
On each page you will see where new posts and comments have appeared.
If you are registered in poker rooms through GipsyTeam, you will receive rake statistics, bonus points for in-store purchases, exclusive promotions and extended support.